Testing candidate data flow across live workflows
A candidate record often moves across three or four systems before a placement is made. It might originate in a sourcing tool, pass into your CRM, sync to email tracking and feed a reporting engine. Each hop creates a potential failure point for data quality, consultant speed and system reliability. Evaluating how these tools integrate before signing a contract prevents costly remediation later.
Trace one candidate record end to end
Select a single active candidate and trace their record through the entire technology stack. The record should enter once, match existing records accurately, and populate the CRM, email logs and job boards without manual intervention. Record every point where a consultant must copy text, export a spreadsheet or reconcile entries manually.
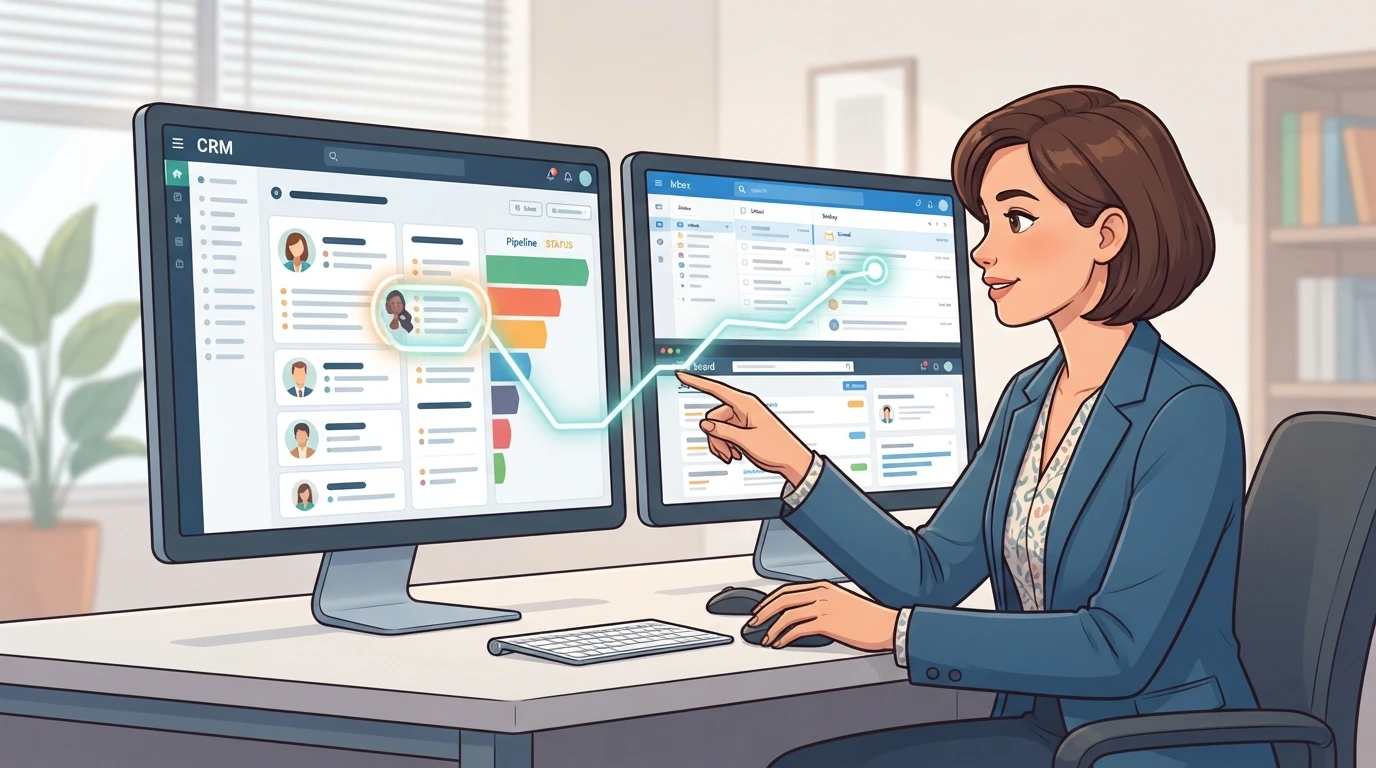
Pay close attention to edge cases. Observe what happens when a candidate submits a second application, emails from a personal address or attaches an updated CV. A well-configured integration processes these updates without creating duplicates or dropping messages. We frequently see agencies lose critical context because emails sent from external client systems fail to extract into the CRM through standard API connections.
Evaluating API reliability and vendor error handling
Ask the vendor to demonstrate how the integration handles system failures. Disconnect a sync endpoint during a live test and monitor system recovery. Determine whether the software retries automatically, flags an error to an administrator or fails silently while operational reports diverge.
API endpoints update, vendor rules change and integration methods are retired over time. Ask suppliers how notice is provided for API updates, who manages schema adjustments and what support costs apply when connections break. A straightforward setup that your internal team can manage usually outperforms a complex build that requires ongoing software vendor intervention.
Checking security evidence against recruitment data risks
A recruitment CRM stores sensitive personal information, including CVs, salary expectations, right-to-work records and interview feedback. Security evaluations must go beyond asking whether a vendor holds certifications. The essential question is whether security controls cover your specific data flows and compliance obligations.
Mapping data movement and access tiers
Map the path candidate data takes across every connected application. Common points of exposure include CV parsing engines, email synchronisation, external enrichment tools and business intelligence layers. Every secondary system represents an additional processor handling candidate records.
Examine access permissions across each tool. Confirm how roles are assigned, whether candidate export functions can be restricted, and what data administrators can access compared to resourcers. When introducing analytics layers or AI tools, verify whether they respect underlying CRM permissions or expose restricted records to unauthorised users.
To evaluate how data moves across your operational stack, reviewing your broader data intelligence service framework helps establish clear baseline standards.
Demanding verifiable security evidence
Sales decks and generic security summaries provide little assurance. Request specific evidence relevant to your agency infrastructure:
- Summaries of recent third-party penetration tests.
- Encryption protocols applied to candidate data at rest and in transit.
- Backup frequency, disaster recovery procedures and defined recovery timeframes.
- Incident notification procedures and contractual reporting timelines.
- Geographic storage locations for primary databases and backup servers.
Validate vendor claims with a small practical check. Create a test candidate record, execute a standard workflow and trace where the data is stored across connected systems.
Validating implementation plans and user adoption risks
Most recruitment software deployments fail several weeks after go-live. Consultants return to private spreadsheets and personal inboxes when system configuration creates friction on the desk. Assessing implementation management during software selection protects your investment.
Defining written acceptance criteria and ownership
Require a detailed written implementation plan from the vendor before committing. The plan should cover data migration timelines, field mapping, integration testing schedules and user training. Verify that internal owners are assigned to every phase and have dedicated time to complete their tasks.
Establish written acceptance criteria that must be satisfied before final sign-off. Measurable standards include verifying that consultant search queries return accurate candidate lists in seconds or that client email notes sync reliably across accounts. When field mappings and duplicate detection rules are left undefined, database quality degrades rapidly.
For agencies planning a system migration or stack overhaul, engaging an independent recruitment technology consultancy ensures vendor commitments match practical operational requirements.
Testing real desk workflows before go-live
Run a structured pilot with two or three experienced billers on active roles prior to full rollout. Require them to log client calls, parse incoming CVs, run Boolean candidate searches and extract pipeline reports. Note any point where consultants experience friction or revert to manual workarounds.
Repeat these operational checks two weeks and six weeks after go-live. System adoption frequently declines after initial training, leading consultants to adopt unofficial habits. Identifying workarounds early allows configuration adjustments before poor data entry habits become established.
Agencies preparing for a platform transition can review our structured approach to CRM implementation service to align technical setup with team adoption.
Balancing review depth against operational constraints
Running a detailed integration and security evaluation requires dedicated effort from leadership and operations staff. Understanding the trade-offs involved helps agency owners focus testing where it matters most.
Key advantages of structured evaluation
Testing software integrations against live agency workflows provides clear operational clarity:
- Identifies manual data rekeying and workflow bottlenecks before contracts are signed.
- Verifies that security and data access controls hold up under real operating conditions.
- Base software selection decisions on observed system performance rather than vendor demonstrations.
- Establishes clear contractual standards for vendor accountability and support boundaries.
Operational constraints to manage
Thorough technical reviews require time from senior team members who hold administrative access. Gathering technical evidence requires asking direct questions of software suppliers, which can lengthen procurement timelines. However, spending several hours evaluating candidate data flows prevents months of operational friction and costly data remediation later.
Establishing evaluation criteria before vendor demonstrations
Evaluating integration reliability, data security and implementation readiness gives agency leaders control over software selection. Before scheduling vendor demonstrations, document your agency's core desk workflows, security requirements and data standards. Establishing objective evaluation criteria ensures your team selects software that supports long-term billings and operational efficiency.
Frequently asked questions
How should a recruitment agency evaluate integration security?
Start by mapping where candidate data moves across your software stack, including parsing tools, email tracking and reporting layers. Request written penetration test summaries, data encryption specifications for data at rest and in transit, and multi-factor authentication requirements. Verify who inside the business can export records or view sensitive candidate information.
How long should a tech stack integration review take?
A focused review typically takes two to three weeks for a small or mid-sized recruitment agency. Spend the first week mapping candidate data flows and defining acceptance criteria. Use the second and third weeks to test real candidate workflows with key billers and evaluate vendor security documentation.
What is the biggest security risk when connecting recruitment tools?
Uncontrolled data proliferation across secondary systems creates the highest risk. When candidate CVs, compensation details and notes sync automatically to third-party tools, visibility controls can be bypassed. Ensuring that third-party integrations respect native CRM permissions and access tiers prevents unauthorised exports and data leaks.
Should recruitment agencies test integrations before buying?
Yes, testing integrations on live candidate records during a pilot is essential. Sales demonstrations obscure edge cases such as duplicate applications, email sync gaps and broken field mappings. Running live placement workflows reveals whether data moves reliably without manual rekeying before contract sign-off.